

ACMP Agent
The agent is deployed to the network clients directly from the ACMP Console. It is required to send Client Commands directly to a client and to maintain continuous communication between the client and the server.
ACMP Kiosk
On this page, you can configure the ACMP Kiosk.
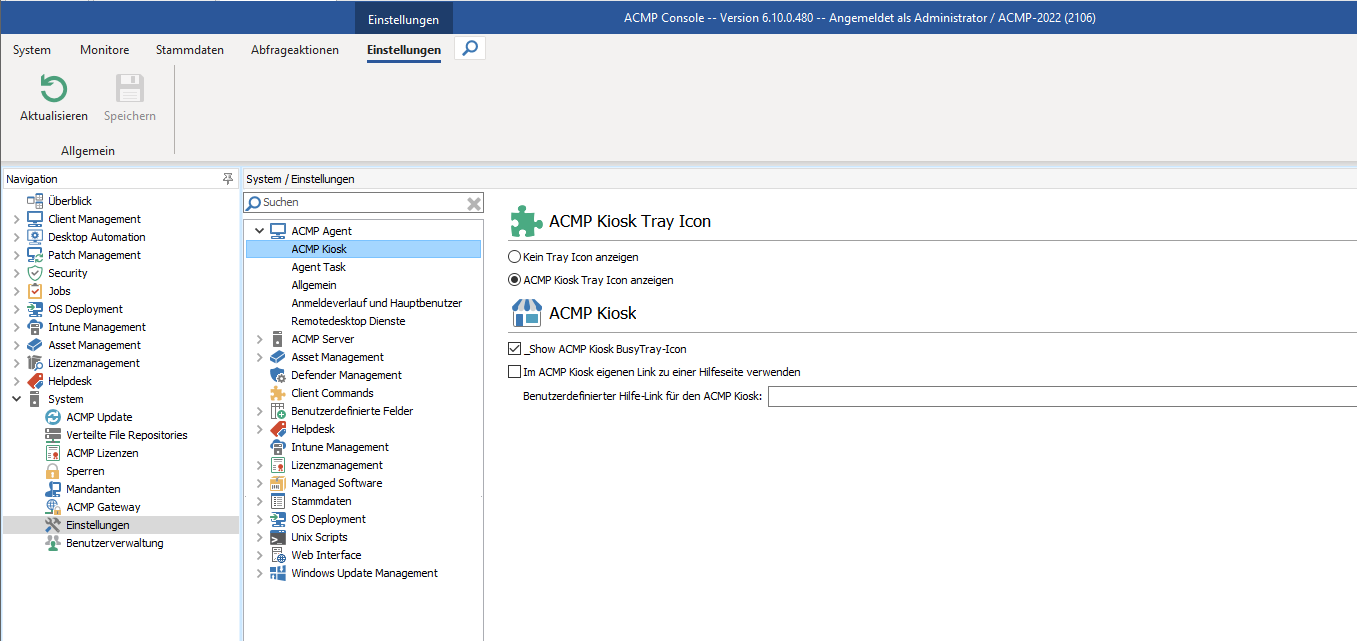
Settings (ACMP Kiosk)
In the General section, you specify the icon properties. You have the following three options:
| Option | Description |
| Do not display a tray icon | As a result, your users will not see a tray icon for either the ACMP Kiosk or the Command Launcher |
| Display ACMP Kiosk Tray Icon | This causes the ACMP Kiosk tray icon to be displayed, replacing the Command Launcher. |
Agent Task
In this section, you can configure the scope of the software scanner and file scanner.
Software scanner
The software scanner assists you in using Licence Management.
You can specify whether the software scanner should ignore updates and system components during the scan. This will reduce the number of results accordingly. You can also specify whether to enable the search for user-specific setup and uninstallation paths. This option is disabled by default. Once activated, the uninstall string will be displayed in the Client Details.
File Scanner
The File Scanner can also assist you with Licence Management, since not all applications leave an entry in the client’s software.
 Note:
Specify whether %WinDir% should be included in the scan. This option is disabled by default during installation. Additionally, specify the file extensions you want to scan for. Here, you can expand the scan to include the following file extensions:
- .exe
- .dll
- .sys
- .jar
Now specify additional devices to be scanned. You have the following options:
- Fixed devices
- Include USB devices
- Removable data drives
- Include USB devices
General
Agent Installation and Network Account
On this page, you first specify the agent installation and network identification account. Here, you can access existing global accounts, create new ones, or specify a specific account. To do so, enter the username and corresponding password in the appropriate fields.
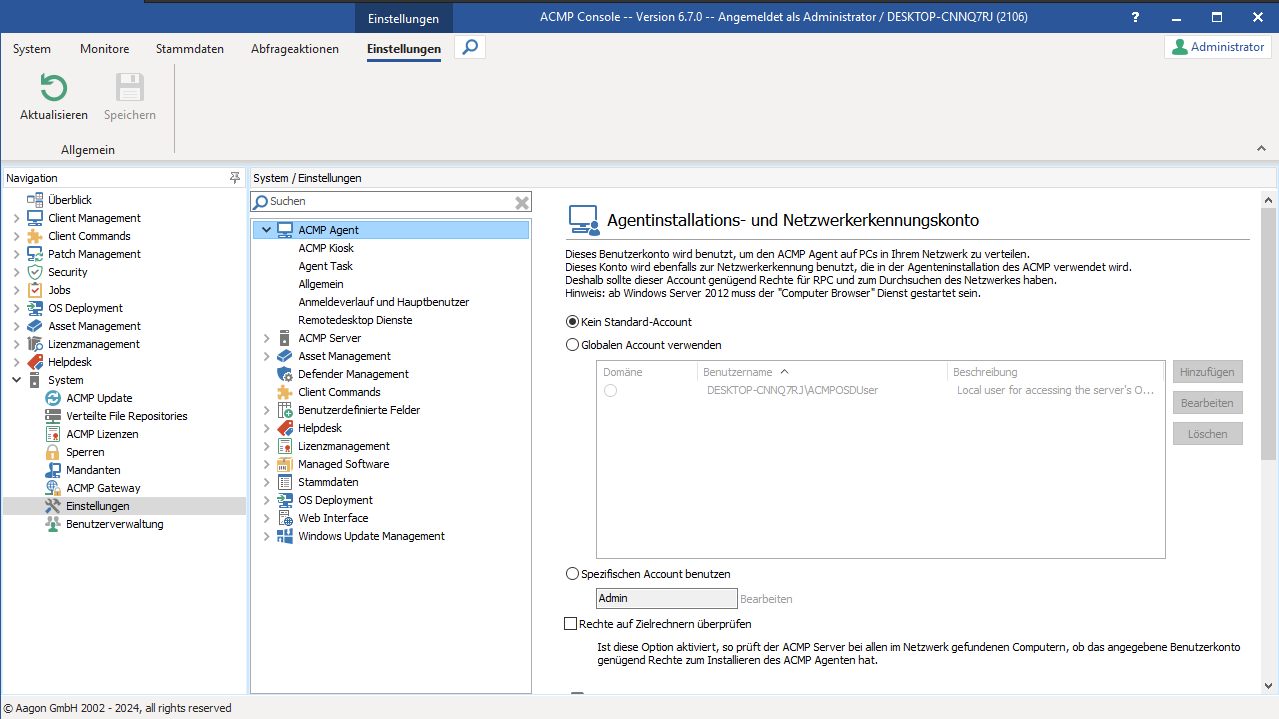
System settings (Agent)
You can specify that the system first check whether the specified account has sufficient rights for installation on all computers found on the network. To do this, select the “Check rights on target computers” checkbox.
Agent Installation Folder
Specify the storage location for the ACMP Agent files. After installation, this is also where you’ll find CommandLauncher.exe, which you can use to launch the Client Command Launcher and execute Client Commands as an alternative to the tray icon.
Client Settings
To uniquely identify computers on the network, ACMP offers various options for Windows and Unix clients. Select the value that is unique on your network.
- Windows Clients:
- Computer SID
- Computer Name
- Primary MAC
- SMBIOS system UUID
- Unix Clients:
- Machine ID
- Computer Name
- Primary MAC
 Warning:
Online Status
The online status feature allows you to define a time period for all client-based queries, which is displayed in the Query Management interface. Here, you can specify the number of minutes after which the client’s last contact with the ACMP Server is no longer considered online. The default value is 60 minutes. Active Clients that are displayed as online in the Query are marked with a green dot; Offline Clients are displayed with a gray icon. Manual Clients, OSC, etc., are not considered online Clients and are displayed without an icon.
If you want to verify the Clients’ online status, you must enable the corresponding checkbox. Only then will the ACMP Agent contact the ACMP Server at the interval you specified.
Job Execution Mode
The job execution mode allows you to configure how jobs should behave once their start condition is met. This currently applies only to jobs of the types “Windows Update Management,” “Managed Software,” and “BitLocker.” Choose between the two available options, Always and Only when changes are applied:
| Option | Description | Example |
| Always | In this mode, the job always runs as soon as the start condition for that job is met. A Job Log is always generated. | A Managed Software job will not make any changes on a client if the same version of the software included in the Managed Software job is already installed. The job log created for this simply indicates that the job ran but that no changes were made. |
| Only when changes are applied | With this option enabled, the job is executed, and a Job Log is created only if the job also performed an update (either for Managed Software or a Windows Update). | With this configuration, there will be no Job Log, since no “actual execution” took place—the software did not need to be updated. |
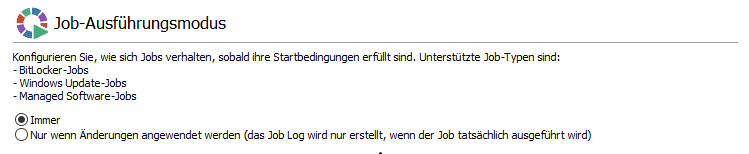
Job Execution Mode for the Start Conditions
Login History and Primary User
In general, you can designate one contact as the primary user for each client. Designating a primary user is generally helpful for quickly determining, in day-to-day operations, which user primarily uses a client. Additionally, designating a primary user is mandatory if you wish to claim the secondary usage right for a client.
There are two ways to designate a primary user for a client: You can either designate the primary user manually or enable automatic primary user detection so that the primary user is determined automatically and dynamically based on logins to the client.
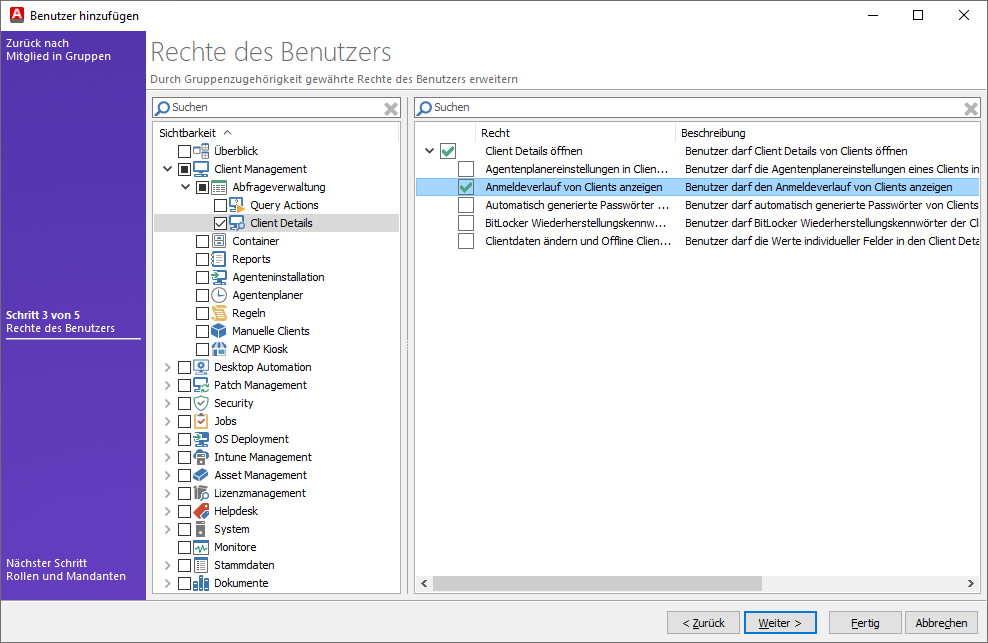
Required rights in user management for using the sign-in history
Manually Designating a Primary User
You can manually designate a primary user in the Client Details. To do this, you must first open a client using a Query and then display the Client Details.
Within the Client Details, navigate to the Linked Contacts entry. There, all contacts currently linked to the client are displayed. The following functions are available in the detail view of the linked contacts:
| Function | Description |
|---|---|
| Add a shortcut | Click this button to open the contact list. From this list, you can then select a contact to link to the client. |
| Delete a shortcut | You can use this button to remove a contact that has already been linked. |
| Reset the primary user | This button deletes the currently active primary user. The Client will then no longer have a primary user. |
You can now select which of the linked contacts should be the client's primary user. To do so, check the checkbox in the Primary User column next to the specific contact.
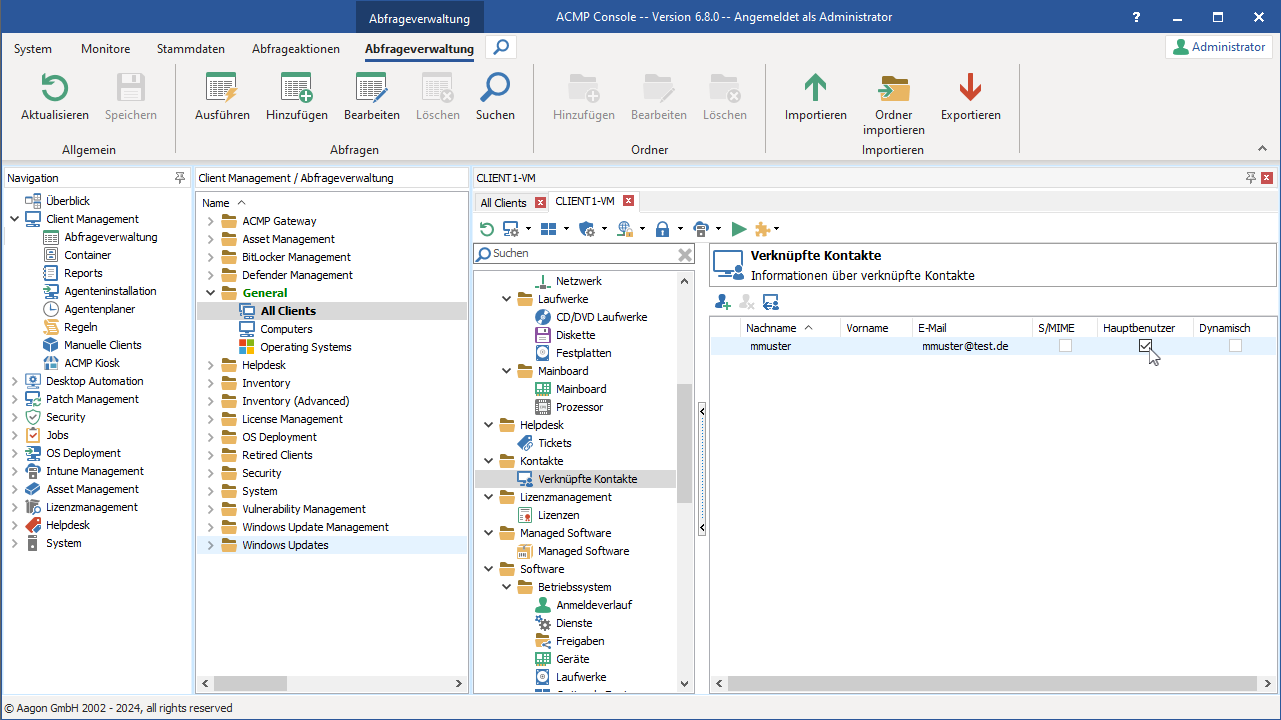
Manually Setting the Primary User in Client Details
Automatic Primary User Detection
With automatic primary user detection, it is possible to automatically and dynamically determine a client’s primary user based on logins to that client. To do this, there are two linked functions in the ACMP Console’s system settings—“Login History” and “Primary User”—that must be enabled for automatic primary user detection.
Erfassung des Anmeldeverlaufs aktivieren
Durch die Aktivierung der ersten Funktion, Scannen des Anmeldeverlaufs, können die Anmeldungen erfasst und gespeichert werden. Es werden ausschließlich “echte” Logins gezählt, also Windows-Logins, bei denen ein vollständiger Session-Aufbau stattfindet. Erfasst werden dabei sowohl RDP-Sessions als auch lokale Anmeldungen.
Beispiel: Es gilt beispielsweise nicht als Login, wenn ein Benutzer sich nach Bildschirmsperre wieder am Client anmeldet.
Nach der Aktivierung können Sie den Anmeldeverlauf des Clients in den Client Details unter dem Ordner Software > Betriebssystem im Eintrag Anmeldeverlauf einsehen. Beachten Sie, dass die Daten für den Anmeldeverlauf über den System Scanner abgerufen werden. Das bedeutet, dass die Speicherung des Anmeldeverlaufs nur für Clients möglich ist, die über den ACMP Agent oder den OneScanClient erfasst wurden.
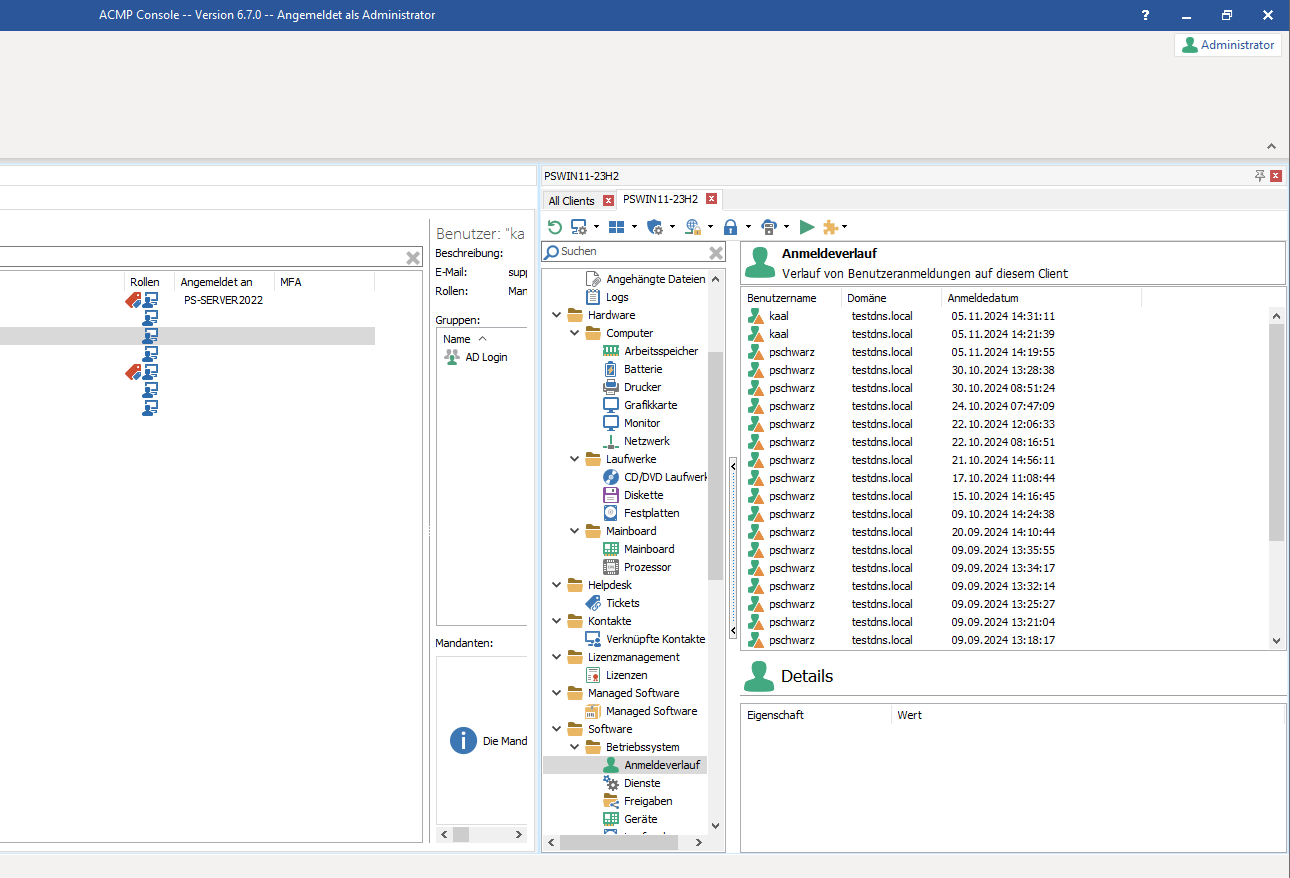
Anmeldeverlauf eines Clients
Für alle Clients, die auf andere Weise erfasst wurden, kann kein Anmeldeverlauf erzeugt werden. Entsprechend muss der Hauptbenutzer weiterhin manuell gesetzt werden, auch wenn die Clients nicht explizit auf der Blacklist stehen.
Ebenfalls können Sie in den Einstellungen festlegen, nach wie vielen Tagen die erfassten Anmeldeverläufe durch einen Server-Job gelöscht werden sollen.
Setzen des Hauptbenutzers aktivieren
Durch die Aktivierung der zweiten Funktion, Hauptbenutzer automatisch setzen, wird ein Benutzer nach einer bestimmten Anzahl an aufeinanderfolgenden Logins automatisch als Hauptbenutzer gesetzt. Die Anzahl der benötigten aufeinanderfolgenden Anmeldungen können Sie in den Einstellungen festlegen.
Durch statisches oder dynamisches Blacklisting ist es möglich, spezifische Clients von diesem Automatismus auszuschließen. Dazu können Sie ausgewählte Clients in den Einstellungen entweder statisch zur Liste der Clients ohne Hauptbenutzer hinzufügen oder Filteroptionen anwenden, um Clients ohne Hauptbenutzer dynamisch zu verwalten.
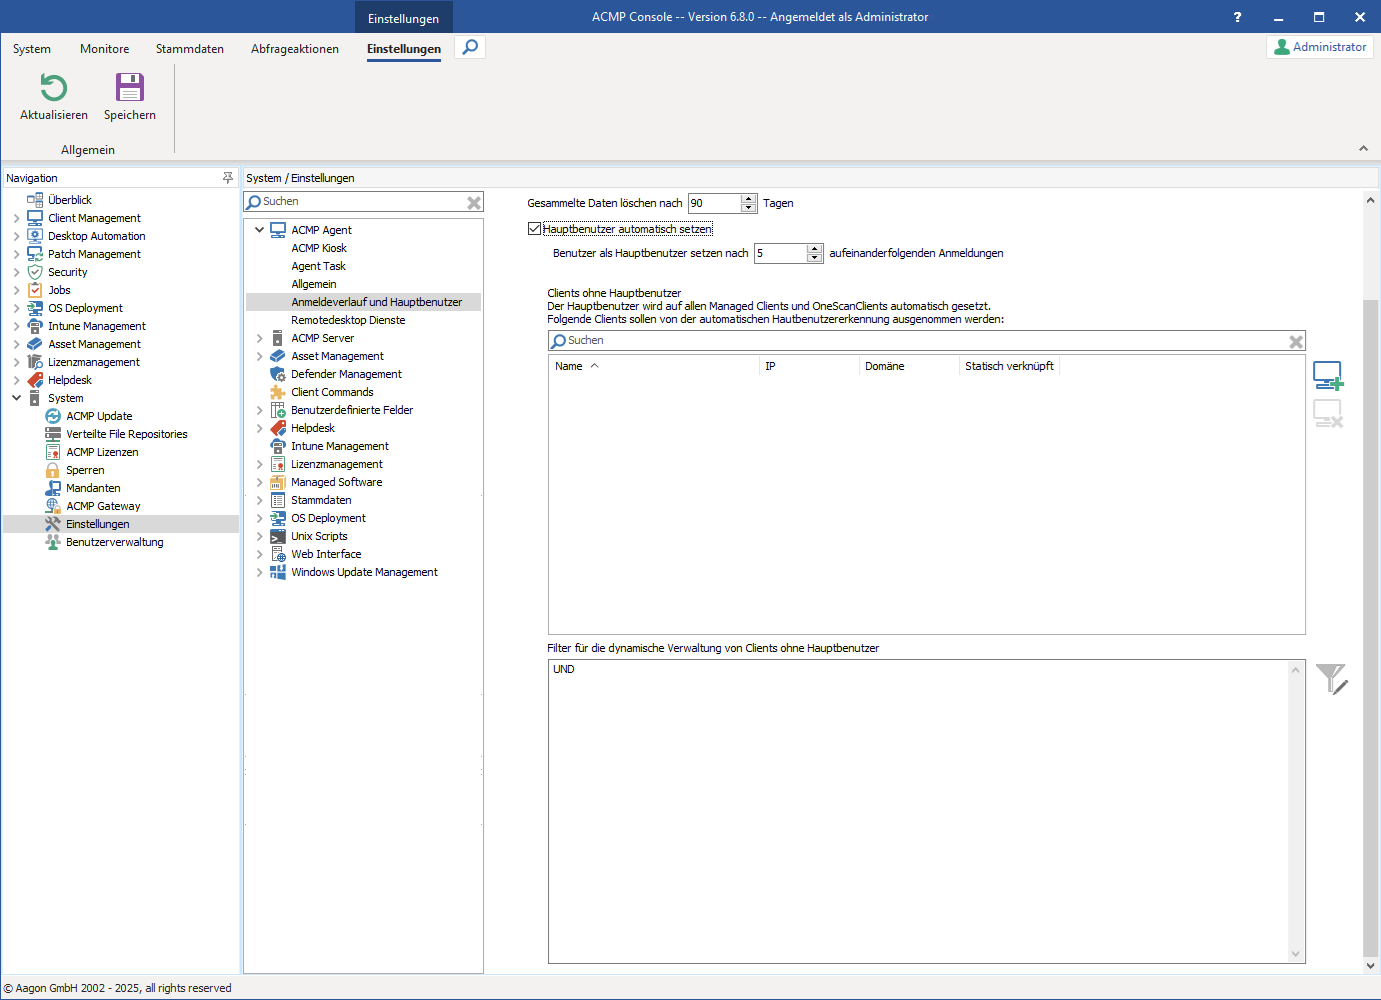
Automatische Hauptbenutzererkennung aktivieren
Sobald Sie die automatische Hauptbenutzererkennung aktiviert haben, wird Ihnen in den Client Details im Eintrag Verknüpfte Kontakte mit einem Banner am unteren Ende des Fensters angezeigt, dass der Hauptbenutzer für den ausgewählten Client automatisch gesetzt wird. Dabei erkennt und merkt sich der Client ebenfalls den Benutzer-Typ. Sofern es sich bei dem Benutzer um einen Active Directory-Benutzer handelt, wird der Kontakt des Benutzers automatisch als verknüpfter Kontakt gelistet und als Hauptbenutzer gesetzt.
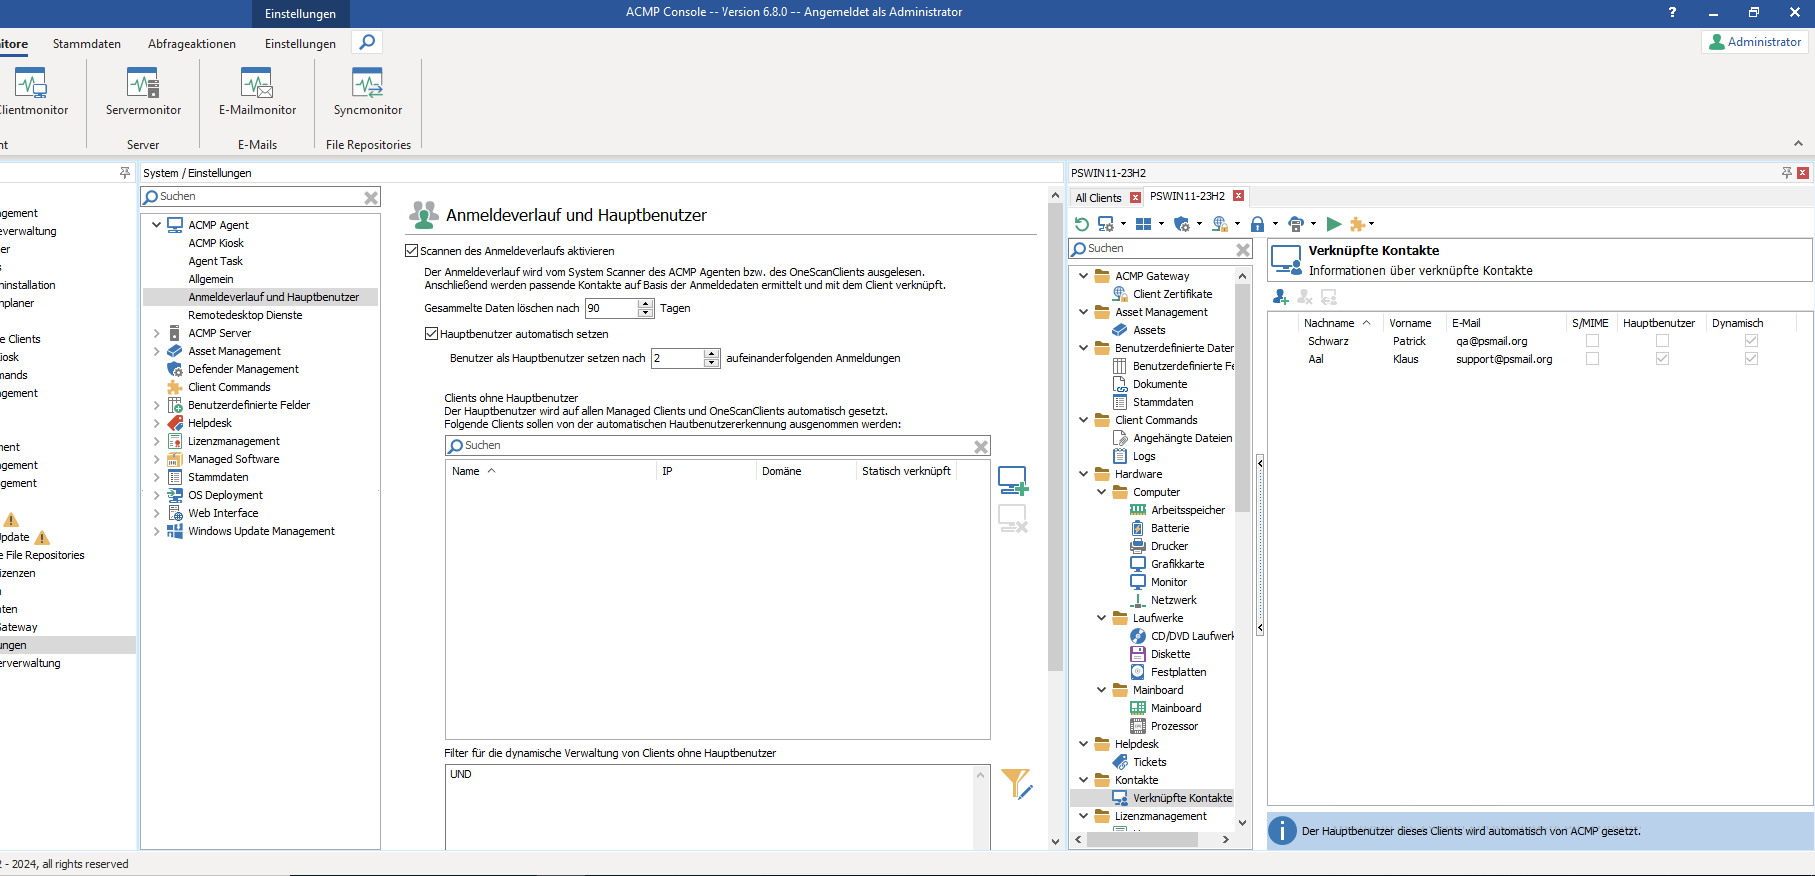
Anzeige des automatisch verknüpften Hauptbenutzers in den Client Details
Sobald die automatische Hauptbenutzererkennung aktiviert ist, ist es nicht mehr möglich den Hauptbenutzer zurückzusetzen oder manuell zu ändern. Sie können weiterhin neue Verknüpfungen manuell hinzufügen und manuell hinzugefügte Verknüpfungen löschen, sofern der verknüpfte Kontakt nicht der Hauptbenutzer ist.
Remotedesktop Dienste
Hier können Sie das Verhalten von erhobenen Daten der Remotedesktop-Verbindungen definieren.
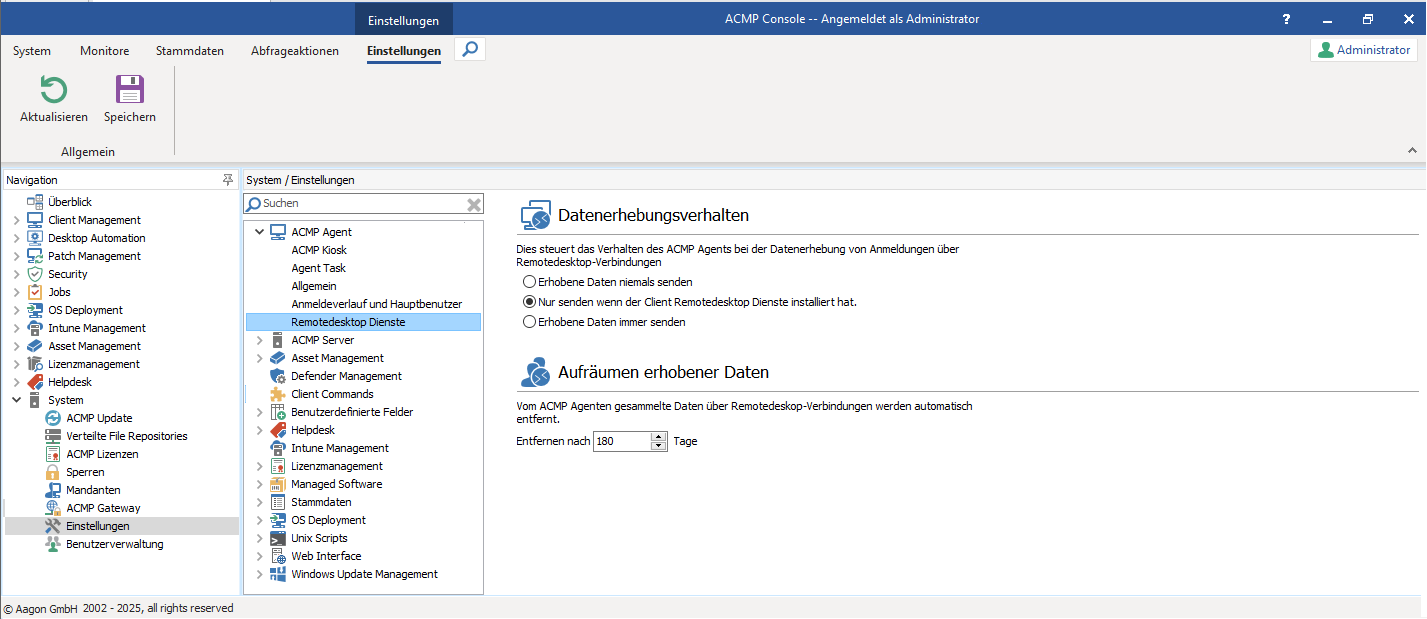
Einstellungen der Remotedesktop Dienste
Aufräumen erhobener Daten
Standardmäßig werden die gesammelten Daten vom ACMP Agenten über Remotedesktop-Verbindungen standardmäßig nach 180 Tagen gelöscht.
Datenerhebungsverfahren
Sie können bei der Remotedesktop-Anmeldung des ACMP Agenten entscheiden, über welches Verfahren die Daten erhoben werden. Aus folgenden drei Möglichkeiten können Sie entscheiden:
- Erhobene Daten niemals senden
- Nur senden, wenn der Client Remotedesktop Dienste installiert hat
- Erhobene Daten immer senden
Standardmäßig ist die Option "Nur senden, wenn der Client Remotedesktop Dienste installiert hat" ausgewählt.